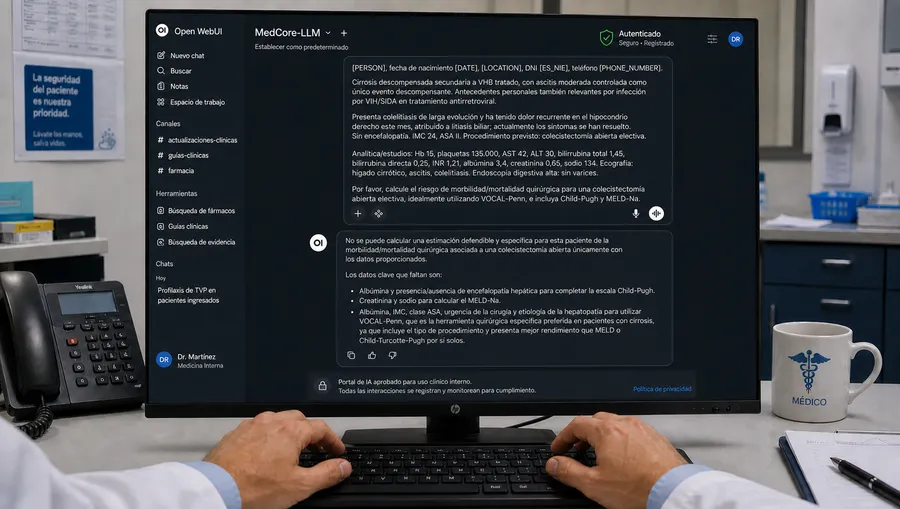
Practical GDPR compliance guidance for healthcare practices in Spain and the EU — data processing requirements, patient rights, AI deployment under Article 35, and subprocessor management.
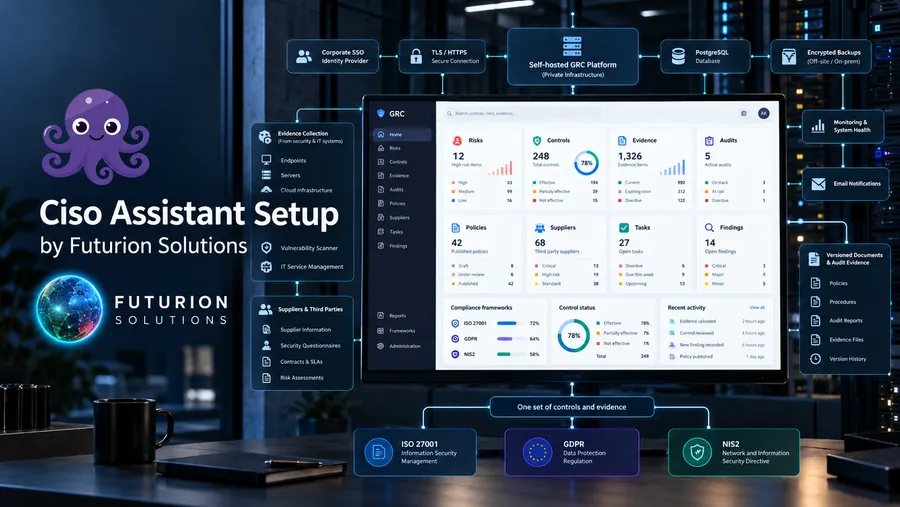
Most CISO Assistant guides stop at the login page. This one starts after it is running and takes a self-hosted install to a usable ISO 27001, GDPR and NIS2 portal, in order.
A customer's ISMS had grown to about 1,660 files in SharePoint. Here is why spreadsheets stop working for IT compliance, and how a self-hosted GRC platform turned it into a live system.
Before deploying any AI in a clinic, GDPR mandates a DPIA. This guide explains what a Data Protection Impact Assessment is, when it is legally required in healthcare, and how to conduct one in seven structured steps.
Healthcare organizations in the EU must track every vendor that touches patient data — including subprocessors. This guide covers the complete workflow for identifying, assessing, and managing third-party data processors under GDPR.
The MIT AI Agent Index 2025 analyzed 30 AI agents and found rapid autonomy growth with weak safety controls. Here is what that means for GDPR compliance when your practice deploys AI automation.
 Futurion Solutions