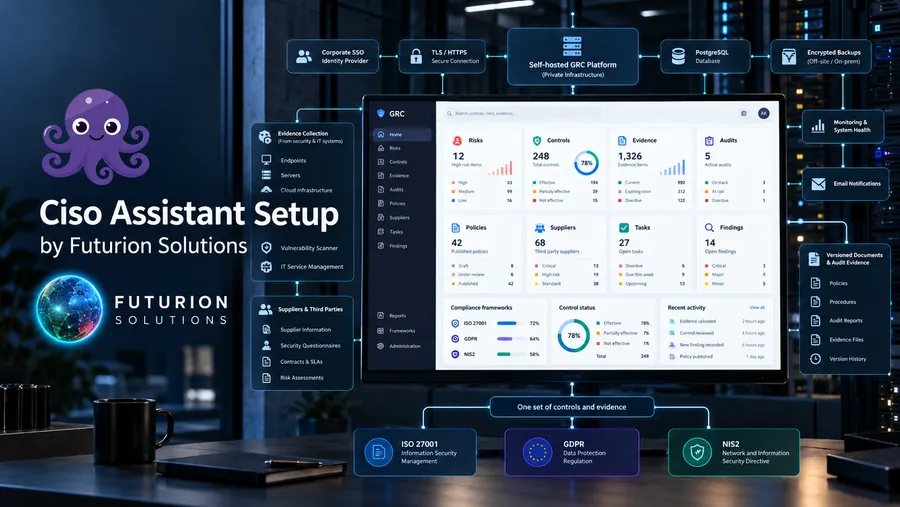
Most CISO Assistant guides stop at the login page. This one starts after it is running and takes a self-hosted install to a usable ISO 27001, GDPR and NIS2 portal, in order.
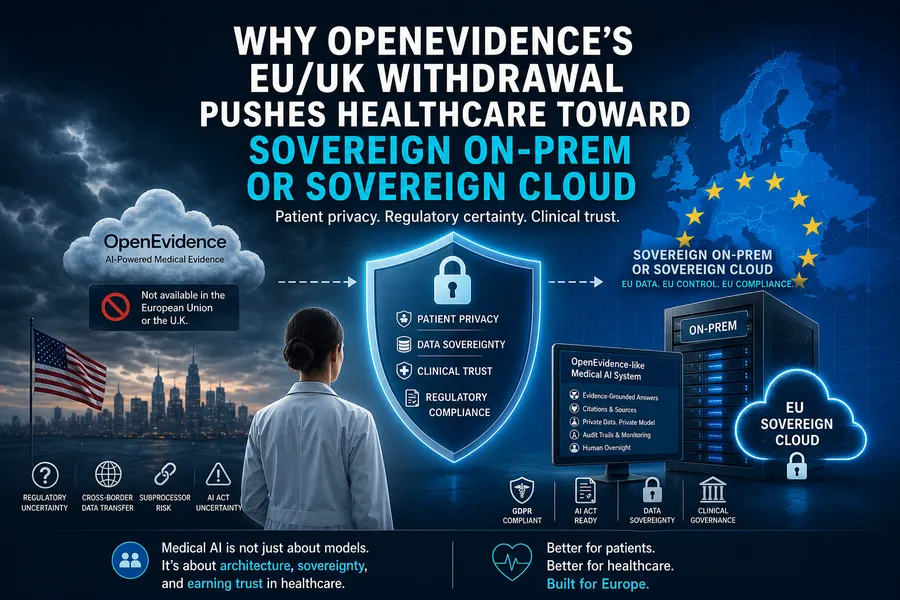
OpenEvidence's EU and UK withdrawal shows why clinical AI in healthcare needs sovereignty, auditability, subprocessor control, and private on-premises or sovereign cloud architecture.
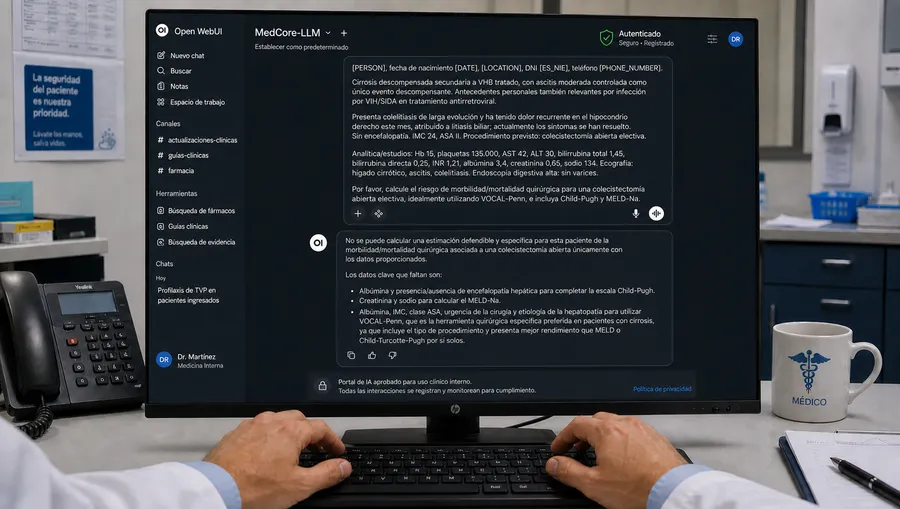
Deploying AI in healthcare is constrained by data residency and regulatory exposure — not model capability. Learn how combining on-premises GPU infrastructure with AWS European Sovereign Cloud (EUSC) satisfies GDPR requirements while enabling rapid, compliant AI deployment.
Before deploying any AI in a clinic, GDPR mandates a DPIA. This guide explains what a Data Protection Impact Assessment is, when it is legally required in healthcare, and how to conduct one in seven structured steps.
 Futurion Solutions